Architecture Review
This guide explains how CloudAEye reviews the architectural impact of a pull request.
Overview
CloudAEye analyzes how a code change affects the system architecture, repository layers, and dependencies when you comment @cloudaeye /review_arch in the PR timeline.
The report shows where the change fits in the existing architecture, identifies architectural issues, and provides questions for further review.
Prerequisites
Step 1: Register
Sign up with CloudAEye SaaS.
Step 2: Setup Code Review
Setup Code Review by following the Getting Started guide.
Initiate Architecture Review
To review the architectural impact of your pull request, comment the following in the PR timeline:
@cloudaeye /review_arch
CloudAEye analyzes the code changes and adds an architecture review report to the pull request.
Architecture Review Report
The report includes:
- An architecture review verdict and the layers affected by the change.
- The system architecture before the change.
- The repository's layers and components.
- Dependencies added or removed by the change.
- Architectural findings and their supporting evidence.
- Impact on other connected repositories.
- Questions that need further review.
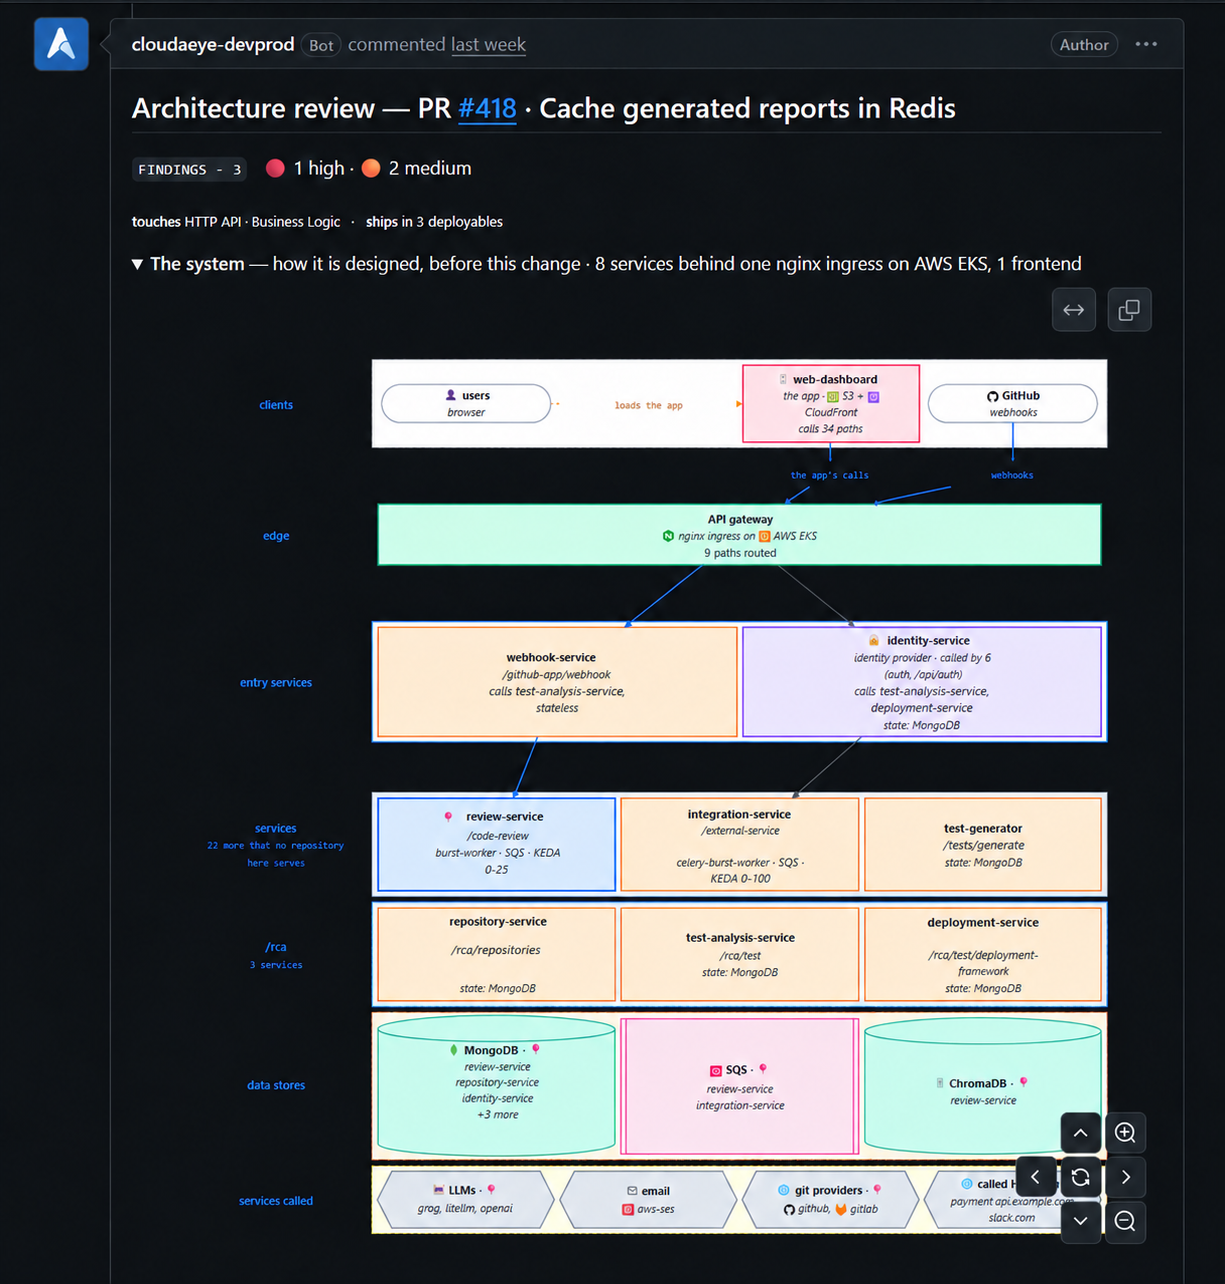
Review Verdicts
| Verdict | Description |
|---|---|
PASS |
No architectural findings were reported for the analyzed change |
FINDINGS |
Architectural findings need attention |
FAIL |
A dependency violates the order of layers explicitly declared by the repository |
Findings on inferred layers include confidence and do not produce a FAIL verdict.
Architecture Findings
CloudAEye checks for:
- Dependencies that run against the layer order.
- New import cycles.
- First-time dependencies on databases, caches, queues, or external services.
- Calls that skip an intermediate layer.
- External packages missing from dependency manifests.
- Modules with unusually many dependents.
- Changes that do not follow the conventions of similar files.
- Changes that affect callers in other connected repositories.
Architecture Review focuses on layers and dependencies. Use Control Flow Analysis to compare call order and Review Code to check for bugs and security vulnerabilities.